What Are the Different Types of Malware? Complete Guide (2026)
The most common types of malware are viruses, keyloggers, worms, trojans, ransomware/crypto-malware attacks, logic bombs, bots/botnets, adware & spyware, and rootkits.

You can reduce or prevent malware attacks by creating security policies, implementing security awareness training, using app-based multi-factor authentication, installing anti-malware and spam filters, adjusting default operating system settings, and conducting routine vulnerability assessments.
It is important to understand that no system is completely “hacker-proof” or free of vulnerabilities. If threat actors have the resources—time, money, and manpower—to carry out an attack, they are nearly guaranteed to find a way in.
There are many different types of malware software, including viruses, worms, trojan horses, ransomware, bots or botnets, adware, spyware, rootkits, fileless malware, and logic bombs. These malicious programs can steal data or encrypt files, and it is important to be aware of the different types in order to prevent them from infecting your computer.
Video: Types of Malware
Malware: What Is It?
“Malware” is short for malicious software. It refers to software created with the intent to damage computers and computer systems. In contrast, software that unintentionally causes harm is considered a software bug or flaw.
People frequently ask what the difference is between malware and viruses. The difference is that malware refers to a wide range of internet threats, including viruses, spyware, adware, ransomware, and other forms of harmful software. One type of malware is a computer virus.
Malware can enter a network through phishing, malicious attachments, harmful downloads, social engineering, and infected flash drives. This guide covers common malware categories.
Most Common Malware Types
To protect yourself from being hacked, it is essential to be aware of the various malware attacks of cyber security. Certain types of malware are well-known, at least by name, while others are not:
1. Adware
“Adware” stands for advertising-supported software. These programs display unwanted and sometimes harmful ads on computer screens or mobile devices, redirect search results to advertising websites, and collect user data that can be sold to advertisers without the user’s knowledge. While some adware is safe and legal, other forms pose risks to endpoint security.
By setting pop-up controls and preferences in their browsers or by using an ad blocker, users may often regulate the frequency of adware or the kind of downloads they permit.
Examples of adware:
- Fireball made headlines in 2017 when an Israeli software vendor discovered it had infected 250 million devices and one-fifth of corporate networks worldwide. Fireball takes over your browser once it infects your PC.
- Appearch is another common adware application that hijacks browsers. It typically comes bundled with other free software and floods the browser with so many ads that using the internet becomes extremely difficult.
2. Spyware
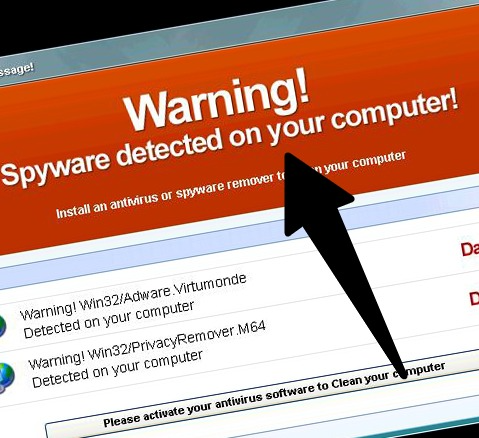
Spyware is malware that hides on your device, monitors your activity, and steals private information such as login credentials, credit card numbers, and other sensitive data. Spyware can spread by exploiting software vulnerabilities, being bundled with legitimate programs, or being hidden inside Trojan horses.
Examples of spyware:
- CoolWebSearch exploited Internet Explorer’s security flaws to take control of the browser, modify its settings, and send browsing information to the program’s creator.
- Gator was frequently installed alongside file-sharing software like Kazaa. It tracked the victim’s web browsing habits and used that data to display targeted advertisements.
3. Crypto-malware and ransomware
Ransomware is malware designed to lock users out of their computers or prevent them from accessing data until a ransom is paid.

Crypto-malware is a type of ransomware that encrypts user files and demands payment by a deadline, often using cryptocurrency like Bitcoin. Ransomware has posed a constant threat to businesses across various industries for many years.
Examples of ransomware:
- CryptoLocker was a type of malware common in 2013 and 2014 that cybercriminals used to access and encrypt system data. They tricked employees into downloading the ransomware onto their computers using social engineering techniques, which then infected the network.
- Phobos ransomware first appeared in 2019. This variant is based on the well-known Dharma (also known as Crysis) family of malware.
4. Trojans
A Trojan (or Trojan Horse) is malicious software that disguises itself as legitimate software to trick you into running it on your computer. Users download it because it appears trustworthy, unknowingly allowing malware to infect their device. Trojans serve as a gateway for other threats.
Examples of Trojans:
- Qbot, also known as “Qakbot” or “Pinkslipbot,” is a banking Trojan that has been active since 2007. It is designed to steal user information and login credentials. Over time, the malware has evolved to include new delivery methods, command and control techniques, and anti-analysis features.
- TrickBot was first discovered in 2016 and was created by skilled cybercriminals. Originally designed as a banking Trojan to steal financial data, it has since evolved into modular, multi-stage malware that provides its operators with a complete toolkit for various malicious online activities.
5. Worms
Worms are one of the most common forms of malware. They spread through computer networks by exploiting vulnerabilities in the operating system. A worm is a self-replicating program that infects other computers without human assistance. Due to their rapid spread, worms are often used to deliver a payload—a piece of code designed to damage a system. Payloads can encrypt data for ransomware attacks, steal information, delete files, or launch botnets.
SQL Slammer was a well-known computer worm that spread without using traditional methods. Instead, it broadcast itself to random IP addresses to find users without antivirus protection. Shortly after it was detected in 2003, more than 75,000 infected computers were unwittingly used in DDoS attacks against various major websites.
6. Viruses
A code that enters an application and runs when launched is known as a virus. A virus can steal sensitive data, conduct DDoS attacks, or carry out ransomware after entering a network. A virus usually spreads through malicious websites, file sharing, or email attachment downloads and lies dormant until the host software or file is activated. Once this occurs, the virus can reproduce and spread across your systems.
One such virus is Stuxnet. When Stuxnet first surfaced in 2010, it was widely believed that the US and Israeli governments had developed it to hamper Iran’s nuclear development. Through a USB flash drive, it gained access to Siemens’ industrial control systems, causing centrifuges to malfunction and self-destruct at an alarming rate. Iran’s nuclear program was put off for years by Stuxnet, which is claimed to have infected over 20,000 computers and damaged one-fifth of its nuclear centrifuges.
7. Keyloggers
A keylogger is a type of spyware that monitors user activities. Keyloggers can be used for legitimate purposes, such as by parents monitoring their children’s internet activities or employers tracking employee behavior. However, when installed maliciously, keyloggers can be used to collect passwords, financial details, and other private data. Systems can become infected with keyloggers through social engineering, phishing, or malicious downloads.
Example of a keylogger:
- A University of Iowa student was sentenced to prison in 2017 after placing keyloggers on staff computers to collect login credentials for manipulating and changing grades. The student was found guilty and given a four-month jail term.
8. Bots and botnets
A “bot” is a computer infected with malware that a hacker can control remotely. The bot, also called a zombie computer, can then launch additional attacks or join a botnet—a network of bots. A botnet may include millions of devices and can spread undetected. Hackers use botnets to carry out DDoS attacks, send spam and phishing messages, and distribute malware.
Examples of botnets:
- The Andromeda botnet was associated with over 80 different malware families. It spread through social media, instant messaging, spam emails, exploit kits, and other channels, infecting huge numbers of new PCs regularly.
- In 2016, a significant DDoS attack disrupted internet service along portions of the US East Coast. Although officials initially suspected a hostile nation-state, the attack was carried out by the Mirai botnet. Mirai targets Internet of Things (IoT) devices and uses them to build its botnet.
9. PUP malware
PUPs, or potentially unwanted programs, are software applications that could contain pop-up windows, toolbars, and advertisements unrelated to the software you downloaded. PUP developers point out that, unlike malware, their programs are downloaded with the users’ consent; therefore, strictly speaking, PUPs are not necessarily malware.
Example of a PUP:
- Mindspark was a PUP that was easy to install and often downloaded onto users’ computers without their full awareness. Once installed, Mindspark could alter settings and initiate actions on the device without the user’s knowledge. It is notoriously difficult to remove.
10. Hybrids
Today, most malware combines multiple types of malicious software, often incorporating elements of Trojans, worms, and sometimes viruses. The malware typically appears to be a Trojan to the end user, but once executed, it spreads across the network like a worm.

Example of hybrid malware:
- In 2001, a malware creator named “Lion” released a worm/rootkit hybrid. Worms spread code quickly, while rootkits give hackers access to operating system files. This combination damaged more than 10,000 Linux systems by exploiting their vulnerabilities.
11. Fileless Malware
Fileless malware uses legitimate applications to infect a computer. Because it does not rely on files and leaves few traces, it is difficult to detect and remove. Fileless malware became a mainstream attack method around 2017, though many of the underlying techniques had existed for some time.
Examples of fileless malware:
- Early examples of this type of malware include Dark Avenger, Number of the Beast, and Frodo.
12. Logic Bombs
A logic bomb is malware that activates only when certain conditions are met, such as a specific date and time or after a certain number of logins. Logic bombs are often embedded in viruses and worms to deliver their payload at a predetermined time or when specific requirements are fulfilled. They can alter data, render hard drives unreadable, or cause other damage.
Example of a logic bomb:
- In 2016, a programmer at a Siemens business branch repeatedly caused spreadsheets to malfunction, forcing the company to keep hiring him back to fix the problem. No one suspected foul play until a coincidence revealed the malicious code.
How is malware spread or introduced?
Email is the primary method used to spread malware. Fraudsters also employ numerous other methods to deliver malware. These are some of the common tactics they use, some of which combine multiple techniques.

- In a browser attack, an attacker injects malware into the system, which secretly installs itself in the browser to record data exchanged between the victim and specific websites.
- Attackers exploit security vulnerabilities by manually searching for weaknesses in devices and networks where malware can be inserted.
- Exploit kits automate the process of finding security weaknesses. These are prewritten scripts that scan for device vulnerabilities and then introduce malware.
- Drive-by downloads occur when users visit a malicious website that hosts an exploit kit, which then delivers malware without the user’s knowledge.
- Social engineering manipulates people’s emotions to get them to click dangerous links, open malicious attachments, or reveal private information. This includes phishing, vishing, and smishing.
How can malware be avoided?
No single solution will stop all malware, as it is pervasive and millions of new malicious files are detected daily. For this reason, using multiple layers of protection for your devices is recommended.
Use Security Software
Here is a list of various malware removal programs that we suggest:
- Bitdefender: Bitdefender is a comprehensive antivirus program that offers strong malware and endpoint protection.
- Malwarebytes: Malwarebytes is a widely used anti-malware program. It performs thorough scans and helps prevent you from running dangerous files or visiting risky websites.
- TitanFile: TitanFile is a secure file-sharing platform that lets you send and receive private information safely. It automatically scans all files for viruses before downloading them to your PC.
- Spybot: Spybot helps guard against spyware by blocking the transfer of your personal information to outside parties.
Be cautious
- You can also prevent malware infections by using caution and common sense:
- Never click on a link in an email that seems suspicious or too good to be true.
- Avoid downloading files from suspicious websites, as they may contain malicious software.
- Avoid using public networks for sensitive business activities on your laptop.
Conclusion
Malware can sometimes cause irreversible damage, such as encrypted or lost files. To protect yourself, keep regular backups of your files so you can restore them if something goes wrong.
References:
https://us.norton.com/blog/malware/types-of-malware
FAQs
What is malware?
Malware, short for malicious software, is designed to harm or damage computers and computer systems. Examples of malware include Trojans, viruses, worms, spyware, adware, and ransomware.
How common is malware?
Malware is extremely common, with new malicious programs appearing constantly. Trojans, ransomware, and other types of malware remain significant threats to both individuals and businesses.
What are the main types of malware?
Malware: Examples of malicious software that can infect your computer include viruses, worms, Trojan horses, spyware, and adware. A virus is a harmful program that replicates itself to damage a computer.